
Customer Data Privacy Policy Template is not just a legal requirement—it’s the cornerstone of trust between a business and its clientele. In an era where data breaches make headlines and consumers increasingly demand control over their personal information, a well‑crafted privacy policy can differentiate a reputable brand from one that simply follows the minimum legal checklist. This blog explores why a robust template matters, what key components it must contain, and how Asian companies can tailor it to local norms while still appealing to an English‑speaking audience.
The Business Case for a Comprehensive Privacy Policy
Every customer interaction, whether a subscription sign‑up, an online purchase, or a casual newsletter request, generates data that can be sensitive, personal, or identifying. A clear, transparent policy does three things: it signals compliance, it boosts customer confidence, and it protects your organization from costly fines. For Asian markets that increasingly adopt global data protection frameworks—such as the EU’s GDPR, Singapore’s PDPA, or China’s Personal Information Protection Law—having a template that addresses each jurisdiction’s nuances is invaluable.
Building Trust Through Transparency
When customers see a privacy policy written in plain language, they are more likely to share information voluntarily. Transparency reduces the perception of hidden agendas, lowers the bounce rate on sign‑up pages, and can directly impact conversion rates. Studies show that sites with well‑structured privacy statements experience a 20% higher trust index among visitors.
Legal Shield and Risk Management
Data protection regulations impose hefty penalties for non‑compliance. A template that covers the legal bases—consent, data retention, data subject rights, third‑party sharing, and breach notification—acts as a first line of defense. It also streamlines audit processes, ensuring that internal teams and external regulators can verify policy adherence without scrambling for documentation.
Competitive Advantage in the Asian Marketplace
Asia is not a monolith; it consists of countries with varying cultural attitudes toward privacy. A template that is customizable to local expectations—such as the emphasis on family data protection in South Korea or the strong emphasis on data sovereignty in Japan—can help businesses resonate with regional audiences while maintaining a consistent brand voice.
Core Elements Every Customer Data Privacy Policy Template Must Include
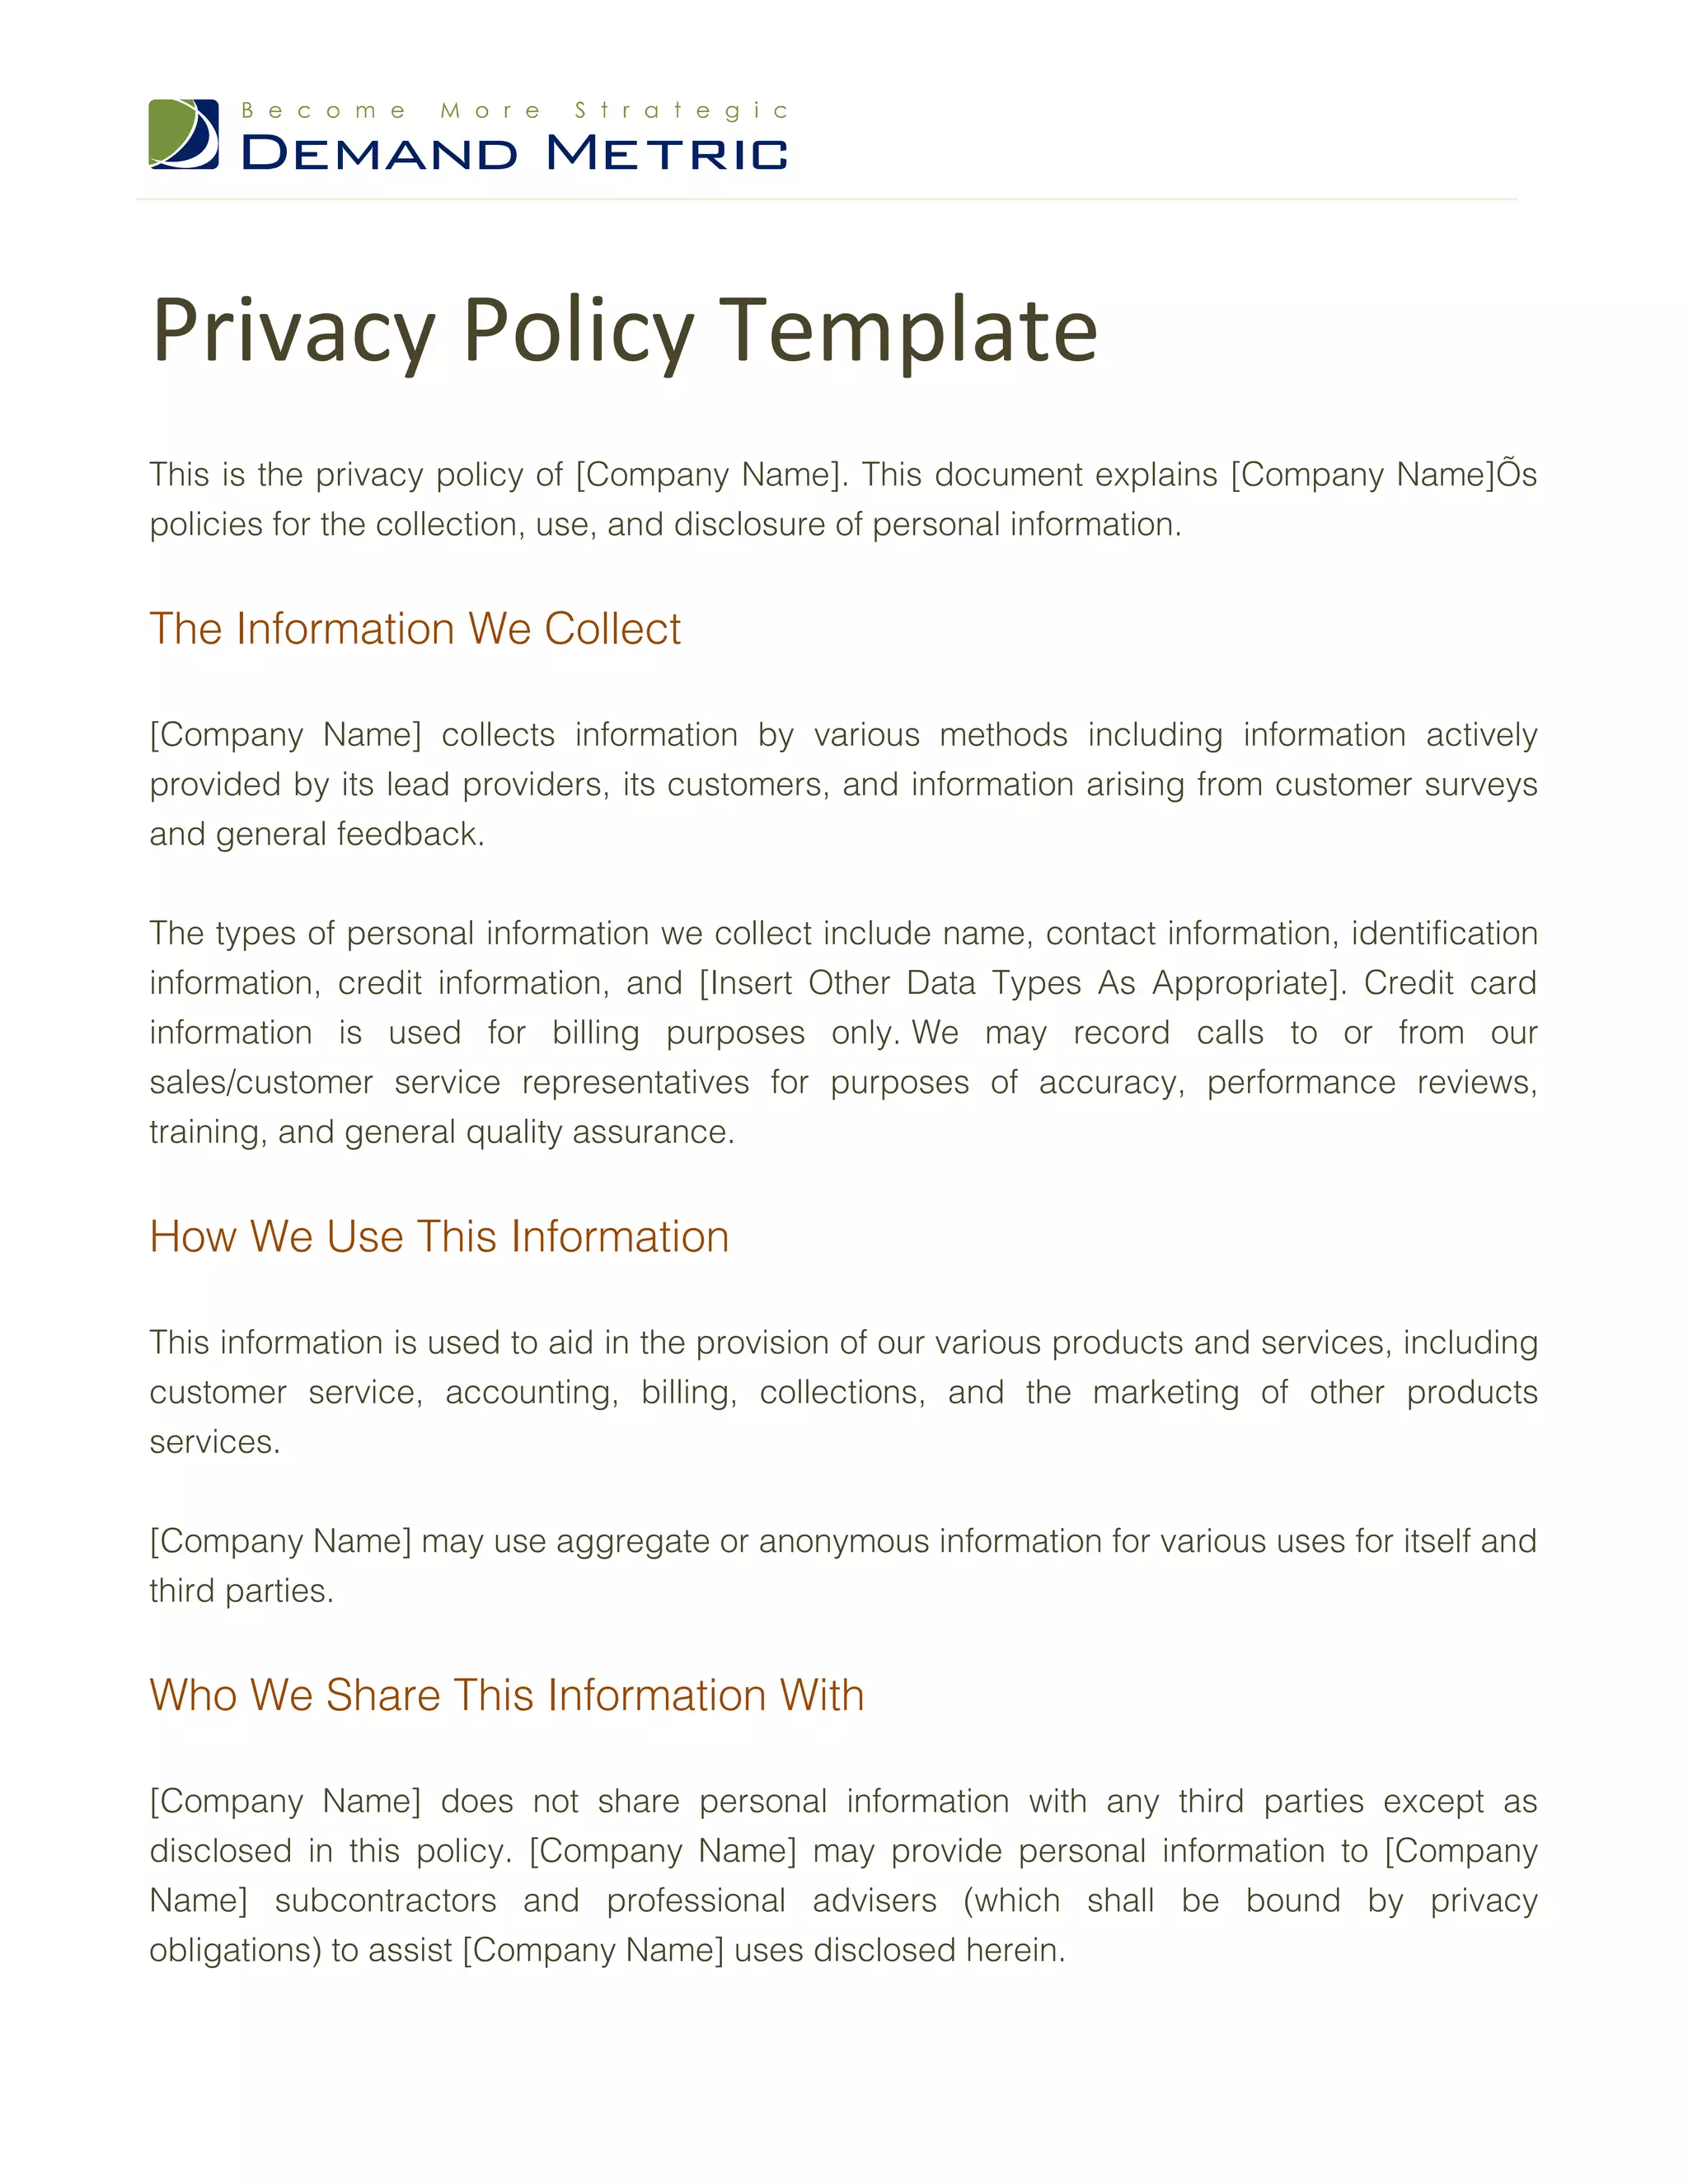
While every company’s data practices differ, certain elements recur in every robust privacy policy. Below is a detailed breakdown that you can adapt to your specific context.
1. Introduction and Scope
This section identifies the company, its legal jurisdiction, and the scope of the policy—whether it applies to all digital interactions, in‑person data collection, or specific products. Clarify that the policy governs all personal information collected from customers worldwide.
2. Types of Personal Data Collected
List and define categories of data: identifying information (name, email, phone), contact details, transactional records, device identifiers, IP addresses, behavioral data, and any sensitive categories relevant to your industry (e.g., health information in a telemedicine startup).
3. Methods of Collection
Explain how data is gathered: website forms, cookies, third‑party analytics, social media integrations, customer support interactions, or offline methods. Provide specific examples of common tools such as Google Analytics, Facebook Pixel, and payment gateways.
4. Purposes and Legal Grounds for Processing
Articulate the legitimate reasons for processing data: providing services, fulfilling legal obligations, improving user experience, or marketing. Use plain language to explain each purpose, and tie them to the legal bases under applicable law (consent, contractual necessity, legitimate interest).
5. Data Sharing and Third‑Party Relationships
Disclose any partners who may receive data—cloud providers, email marketing platforms, payment processors. Include the nature of the shared data and the safeguards in place, such as data processing agreements or confidentiality clauses.
6. Data Retention Policy
State how long personal data will be stored and the criteria for determining retention periods. Provide transparency on when and how data will be securely disposed of or anonymized.
7. User Rights and How to Exercise Them
List the rights available to customers: access, correction, deletion, restriction of processing, portability, and objection. Explain the process to submit requests, including contact details, required verification, and expected response times.
8. Security Measures
Outline technical and organizational controls such as encryption, access controls, regular audits, and employee training. Highlight compliance with industry standards like ISO 27001 or SOC 2 where applicable.
9. Breach Notification Procedures
Detail how a breach will be identified, investigated, and communicated. Include timelines (e.g., 72 hours under GDPR), contact information for affected customers, and steps the organization will take to mitigate harm.
10. Contact Information and Policy Updates
Provide a dedicated privacy contact, such as a Data Protection Officer. Explain how customers will be notified of significant updates—through email, website banners, or social media posts.
Step‑by‑Step Guide to Crafting Your Own Customer Data Privacy Policy Template
Follow these practical steps to transform the framework above into a fully customized policy that reflects your brand’s voice and regulatory obligations.
1. Conduct a Data Mapping Exercise
Identify all data flows within your organization. Use tools like a data inventory spreadsheet or automated data mapping software. Document sources, storage locations, and destinations.
2. Align with Legal Requirements
Research the applicable data protection laws in every market you operate. Create a compliance matrix that aligns each legal requirement with the corresponding policy section.
3. Draft the Policy Using Plain Language
Avoid legalese. Use short sentences, active voice, and everyday terminology. For instance, replace “The entity shall not store personal data beyond a period of ten years” with “We won’t keep your information longer than ten years unless you’re a repeat customer.”
4. Incorporate Cultural Nuances
Incorporate phrases that resonate locally—such as references to “family data” in Korean contexts or “data sovereignty” in Japan. This shows sensitivity to regional concerns and can increase adoption rates.
5. Review with Stakeholders
Engage legal counsel, IT security teams, and marketing departments to verify accuracy. Ask non‑technical staff to read the draft and suggest improvements for clarity.
6. Publish and Promote
Place the policy at a prominent location on your website, such as a footer link or a dedicated privacy page. When customers sign up, provide a clear checkbox for consent and a link to the full policy.
7. Monitor, Update, and Communicate
Set a quarterly review schedule to ensure the policy remains aligned with evolving laws and business practices. Notify customers promptly when significant changes occur.
Tailoring the Template for Asian Markets
Asian countries have distinct regulatory landscapes and consumer expectations. Below are region‑specific considerations.
1. Japan – Data Sovereignty and Consent
Japan’s Personal Information Protection Commission emphasizes explicit consent for data collection, especially for marketing purposes. Include a clear opt‑in mechanism and detail how data will be stored within Japanese borders or with local cloud providers.
2. South Korea – Family Data Protection
South Korea’s Personal Information Protection Act recognizes “family data” as a sensitive category. If your service involves family members, provide a section that explains how you handle data for minors or dependents and the safeguards in place.
3. Singapore – PDPA Compliance
Singapore’s PDPA requires a notice statement at the point of data collection. Embed a short summary within the consent form and link to the full policy. Highlight the rights to request data correction or deletion.
4. China – Data Localization and Security
China’s PIPL mandates that personal data must be processed in China or with Chinese partners if it’s considered “sensitive.” Include a clause that explains whether your data centers are located domestically and how cross‑border transfers are secured.
5. ASEAN – Harmonizing Across Jurisdictions
Countries like Indonesia and Malaysia have their own evolving frameworks. A modular template that allows you to toggle country‑specific sections can help you remain compliant without rewriting the entire document.
Real‑World Examples of Effective Privacy Policies
Examining successful templates can provide inspiration for your own.
Example 1: E‑commerce Startup
This policy uses a flowchart in the footer that guides users through each step of the purchasing process, showing what data is collected at each point. The language is conversational, and a “Frequently Asked Questions” accordion section addresses common concerns.
Example 2: SaaS Platform
Here, the privacy policy is integrated into the user dashboard. Whenever a user updates settings, a pop‑up highlights changes to data usage. This proactive approach keeps the policy in the user’s line of sight.
Example 3: Mobile App for Food Delivery
The policy includes a section on “Location Data” with clear explanations of why GPS information is required for delivery accuracy. It also offers an opt‑out for non‑essential analytics, respecting privacy without hindering core service functionality.
Best Practices to Maximize Policy Effectiveness

Beyond drafting, the real test lies in execution and ongoing management.
1. Use Clear, Short Paragraphs
Break up dense legal text into bite‑size chunks. Bullet points, icons, and callouts can help readers quickly locate information.
2. Keep the Tone Consistent
Match the policy’s voice to your brand identity—professional yet approachable. This consistency reinforces authenticity.
3. Provide a Data Subject Request Form
Instead of a generic email address, offer a dedicated portal where users can submit requests and track their status. This reduces friction and improves compliance.
4. Conduct Regular Privacy Audits
Schedule annual or semi‑annual reviews with IT and legal teams. Use audit checklists to verify that data processing aligns with policy statements.
5. Train Employees on Data Privacy
Internal training programs ensure that everyone—developers, marketers, customer service—understands the policy and follows best practices.
6. Leverage Technology for Transparency
Deploy privacy management platforms (PMPs) that automate consent tracking, data subject request handling, and policy versioning.
Conclusion: Turning a Template into a Trust Engine
A Customer Data Privacy Policy Template is more than a compliance checklist; it is the foundation upon which trust, credibility, and long‑term customer relationships are built. By incorporating clear definitions, robust legal coverage, and culturally sensitive language, Asian businesses can protect themselves against regulatory penalties while resonating with diverse audiences. The key is to treat the policy as a living document—regularly revisiting, updating, and communicating changes to keep pace with evolving technology and law. With a well‑crafted privacy statement in place, your organization can focus on growth, confident that customer data is handled responsibly, ethically, and with the highest level of transparency.
[ssba-buttons]